Insights

Merito Insights

Fresh thinking on secure software delivery, DevOps best practices, and the people-first approach that powers our clients’ success.

Picture showing Engineer Protecting Against AI Cyber Threats with title "The 4 Things Every AppSec Vendor Now Ships, and the 4 We Still Need to Solve" and subtitle "Triage, autofix, IDE integration and grounded output are now table stakes. Re-testing, AI-BOM, mobile and agent guardrails will decide the next 12 months." with Blog Pill and Merito Logo
Application Security and DevSecOps

AppSec for the AI Era: What's Converged, and What's Still Taking Shape

AppSec vendors have converged on exploitability-scored triage, autofix pull requests, coding-agent integration, and grounded output, making those four things table stakes, not differentiators. Real competitive separation over the next 12 months will happen in four unsolved areas: continuous re-testing after a fix ships, AI-BOM, mobile AppSec keeping pace with embedded AI, and agent guardrails that enforce policy at the execution harness, not just the agent's decisions.

  • Application Security
  • AI
  • AI Coding
  • DevSecOps
  • SBOM
  • SCA
  • Compliance
artificial intelligence used for testing automation
Test Management and Traceability

Bring Live SpiraPlan Quality Data into XWiki Documentation

Inflectra's beta SpiraPlan Extension for XWiki embeds live SpiraPlan requirements, test cases, releases, and defect backlogs directly in XWiki pages. Enterprise teams can use it to keep project documentation connected to current quality management data and support a shared view of delivery status. Merito helps organizations assess fit, plan adoption, and align XWiki and SpiraPlan workflows with governance needs.

  • Inflectra
  • SpiraPlan
  • GenAi
Merito blog cover for Claude Fable 5.1 Cache Price Cut and Your AI Bill, by Chris Carpenter
AI in Software Delivery

What the Claude Fable 5.1 Cache Price Cut Actually Does to Your AI Bill

Claude Fable 5.1 reduced prompt cache read pricing to $0.25 per million tokens while input stayed at $10 and output stayed at $50 per million. Because only the cache read price adjusted, a customer's actual savings equals roughly 75% of the share cache reads of their current bill, which is why Anthropic quotes the range from 25% on typical workloads to 45% on agentic ones. This post shows the arithmetic and equation, works it through a fifty-engineer coding agent example, and covers the three patterns that ruin the savings.

  • AI
  • Enterprise AI
  • AI Adoption
  • AI Coding
  • GenAi
  • Procurement
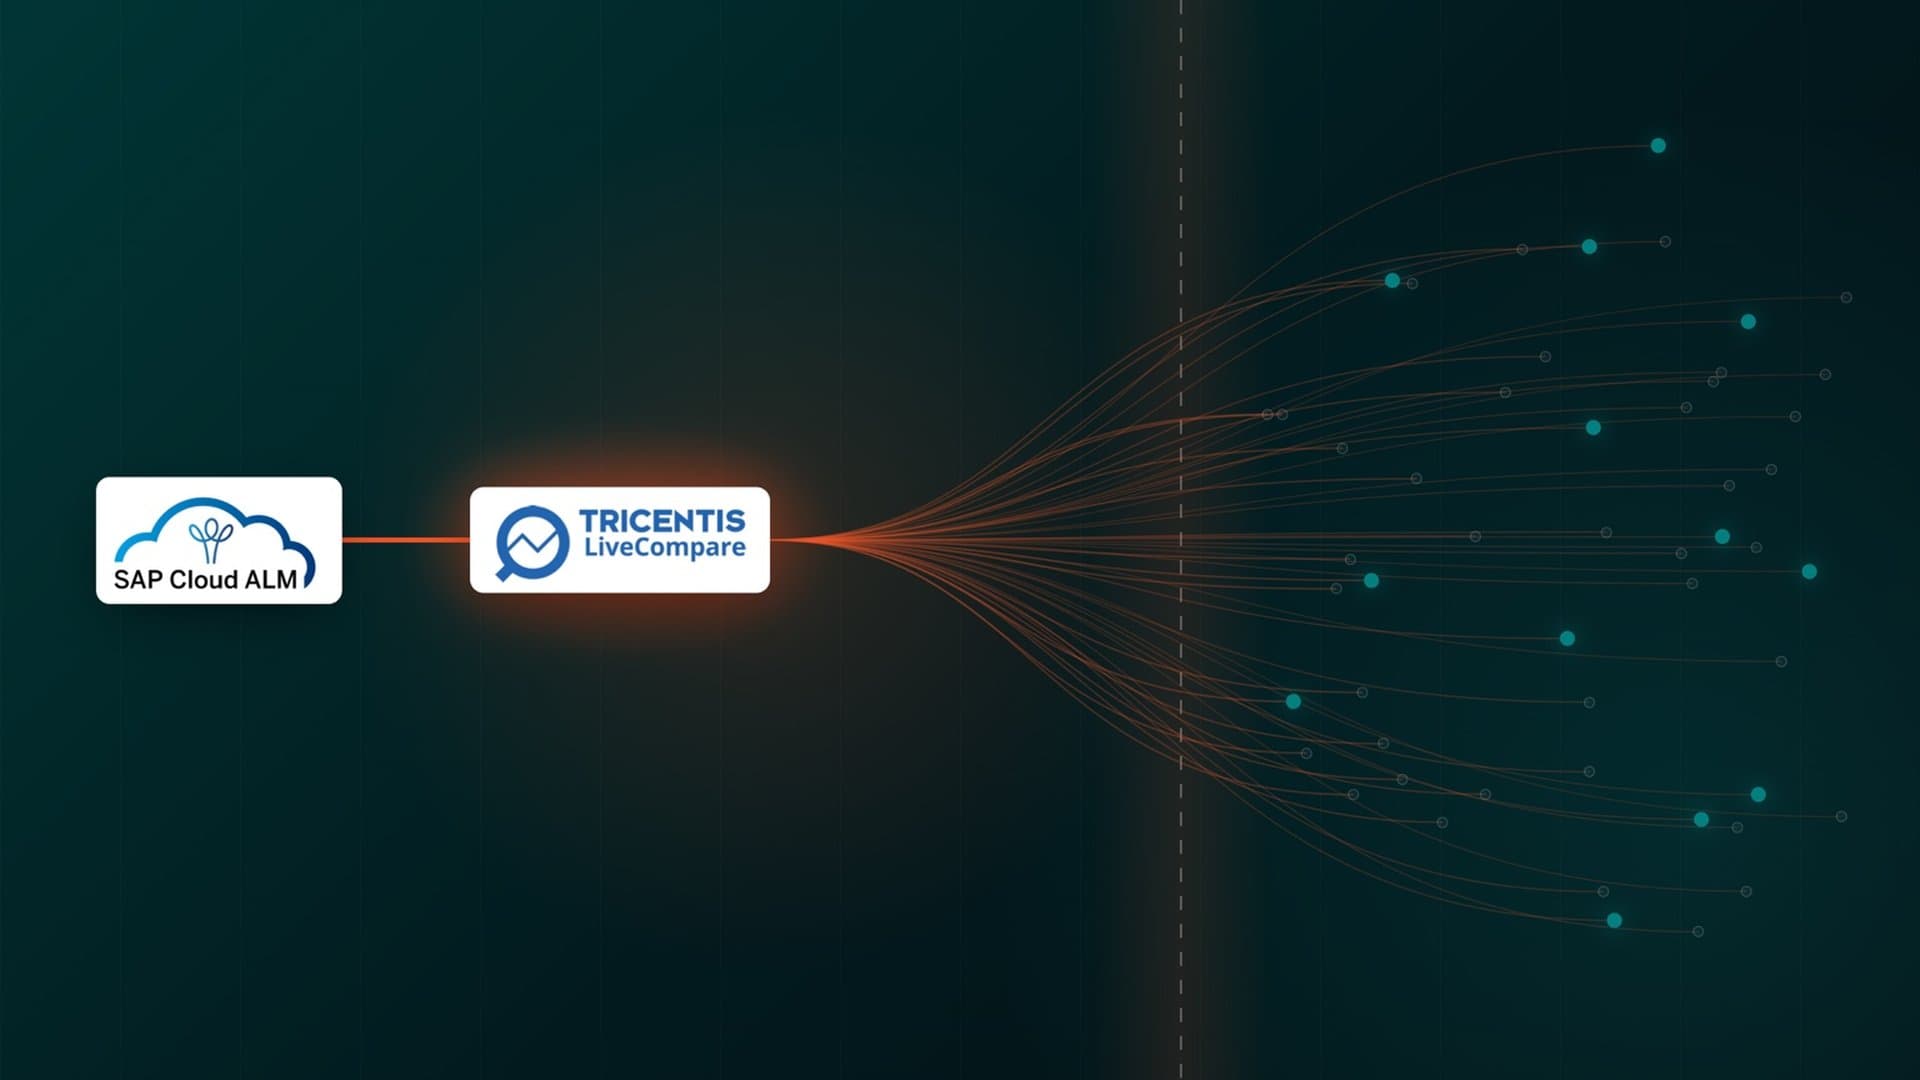
SAP Cloud ALM feeding Tricentis LiveCompare to analyze SAP transport changes and identify affected business processes for targeted testing.
SAP Testing

You Test Everything Because Nobody Can Prove What the Transport Touched

SAP Change Impact Analysis (CIA), sold by Tricentis as LiveCompare, reads a transport, support pack, or upgrade delta and resolves every dependent object down the call structure, standard SAP code included. It weights that dependency graph with production usage so objects nobody calls drop out of scope, then matches the result against test repositories such as Tosca, qTest, or Solution Manager to return covered objects and coverage gaps. Run on every transport cycle it makes a SAP Cloud ALM release gate enforceable instead of a signature field.

  • SAP
  • S/4HANA
  • SAP Upgrade
  • Tricentis
  • SAP Testing
  • Test coverage
  • Audit
  • Compliance
  • SDLC
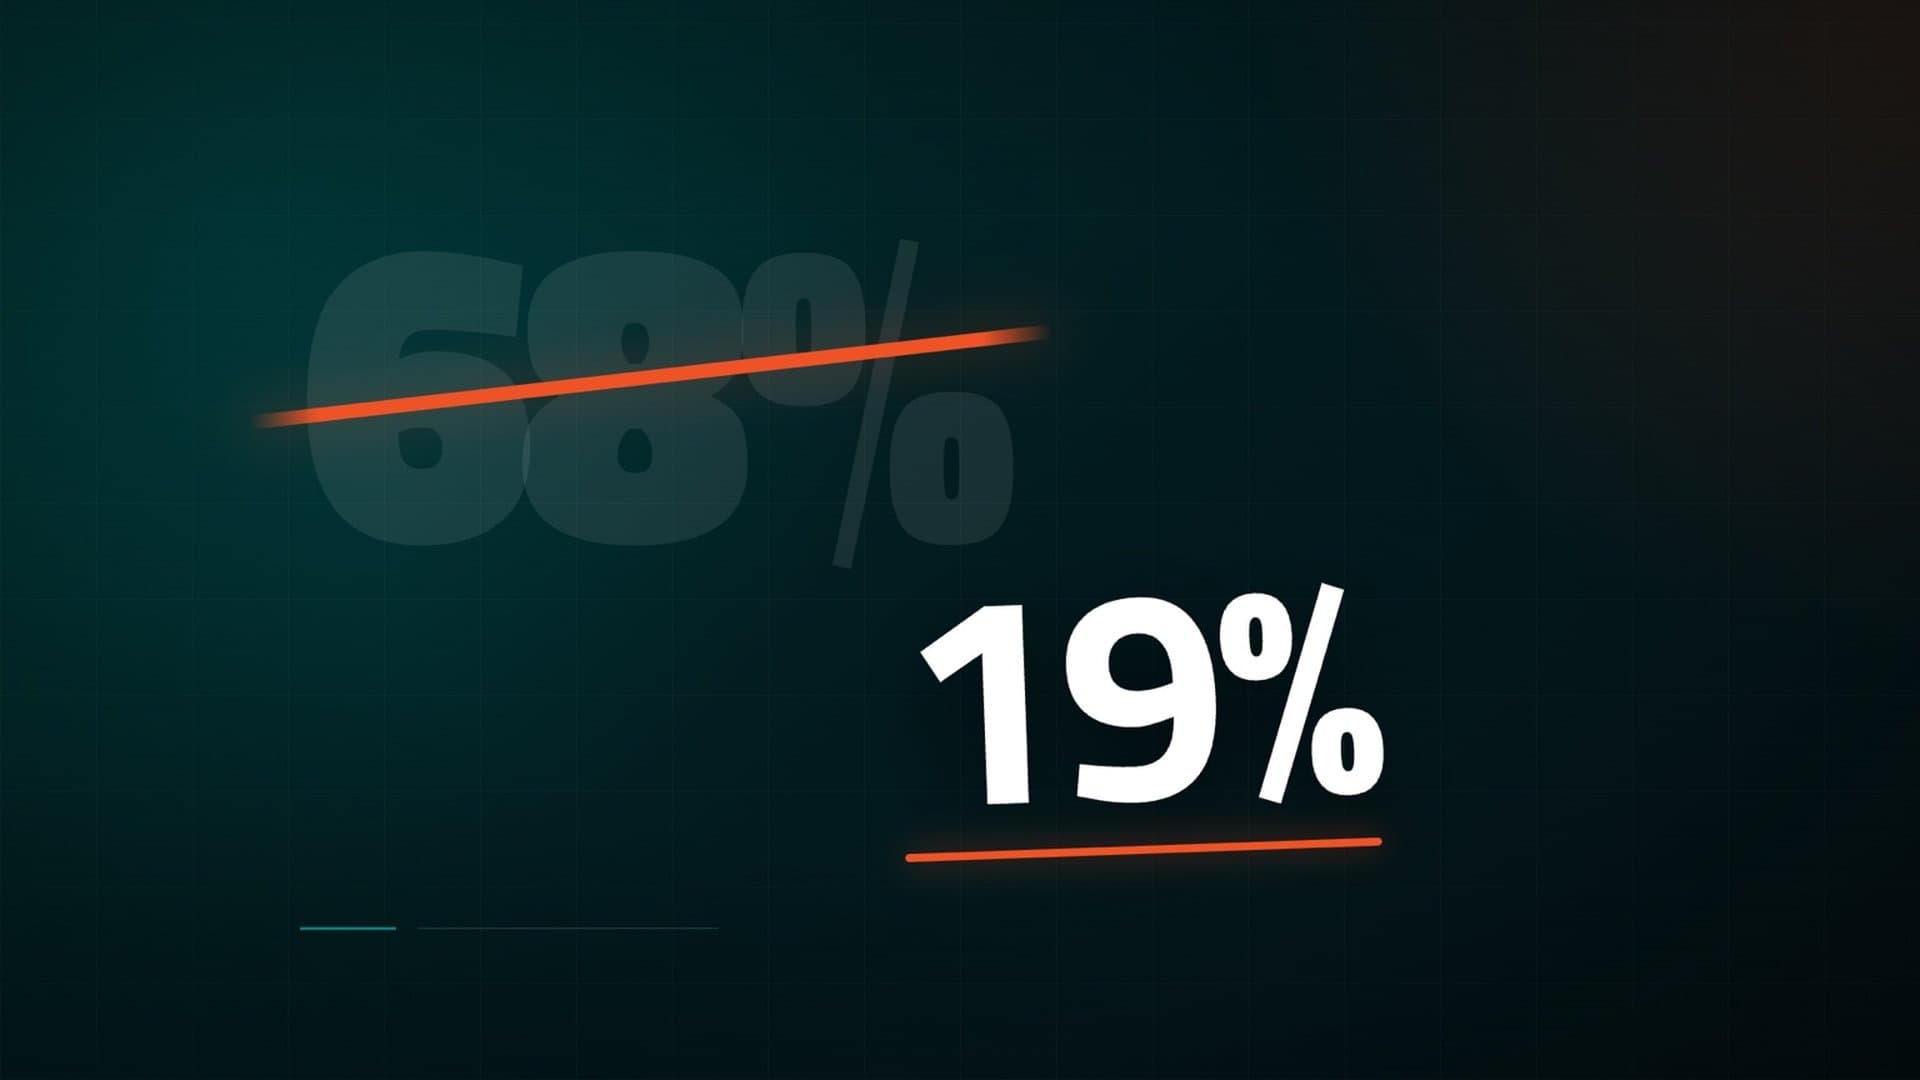
Graphic showing a 68% value crossed out and replaced with 19%, illustrating a significant reduction or improvement in an application quality metric.
SAP Testing

Your SAP Change Impact Business Case Needs Five Numbers, and None of Them Come From a Vendor

A business case for SAP change impact analysis should rest on five numbers the team produces itself: the fully loaded cost of one regression cycle, the number of cycles run per year, the share of test cases that exercise an object a transport actually changed, a scope reduction the team would defend to a CFO, and the price of one escaped defect. Vendor-published ROI percentages collapse under finance scrutiny because they trace back to a product page rather than the buyer's own program, and the escaped-defect line is usually the largest item in the model.

  • SAP
  • SAP Test Automation
  • SAP Upgrade
  • Tricentis
  • Procurement
  • Software Licensing
  • Enterprise Testing
  • Compliance
Stop sign
Buying and Licensing Software

STOP: Don't Buy Tricentis Licenses

Most Tricentis rollouts, whether Tosca, qTest, or NeoLoad, stall after the purchase order is signed, and the licensed seats quietly turn into shelfware. The license is the cheap part. The real cost is the faster regression, fewer defect escapes, and lower rework you paid for but never operationalized. Buying Tricentis through a partner like Merito closes the gap between purchase and payoff, and often lands a lower price than going direct.

  • Tricentis
  • Test Automation
  • Software Licensing
  • Shelfware
  • Procurement
EHR test automation
Test Automation

AI-powered EHR test automation and compliance done right!

Healthcare organizations use Epic test automation to validate critical workflows, reduce upgrade risks, protect revenue cycles, and ensure patient safety. Merito helps enterprises build and manage scalable Epic QA automation frameworks.

  • Epic
  • Healthcare
  • EHR

Frequently Asked Questions

Questions about the Merito blog