Insights

Merito Insights

Fresh thinking on secure software delivery, DevOps best practices, and the people-first approach that powers our clients’ success.

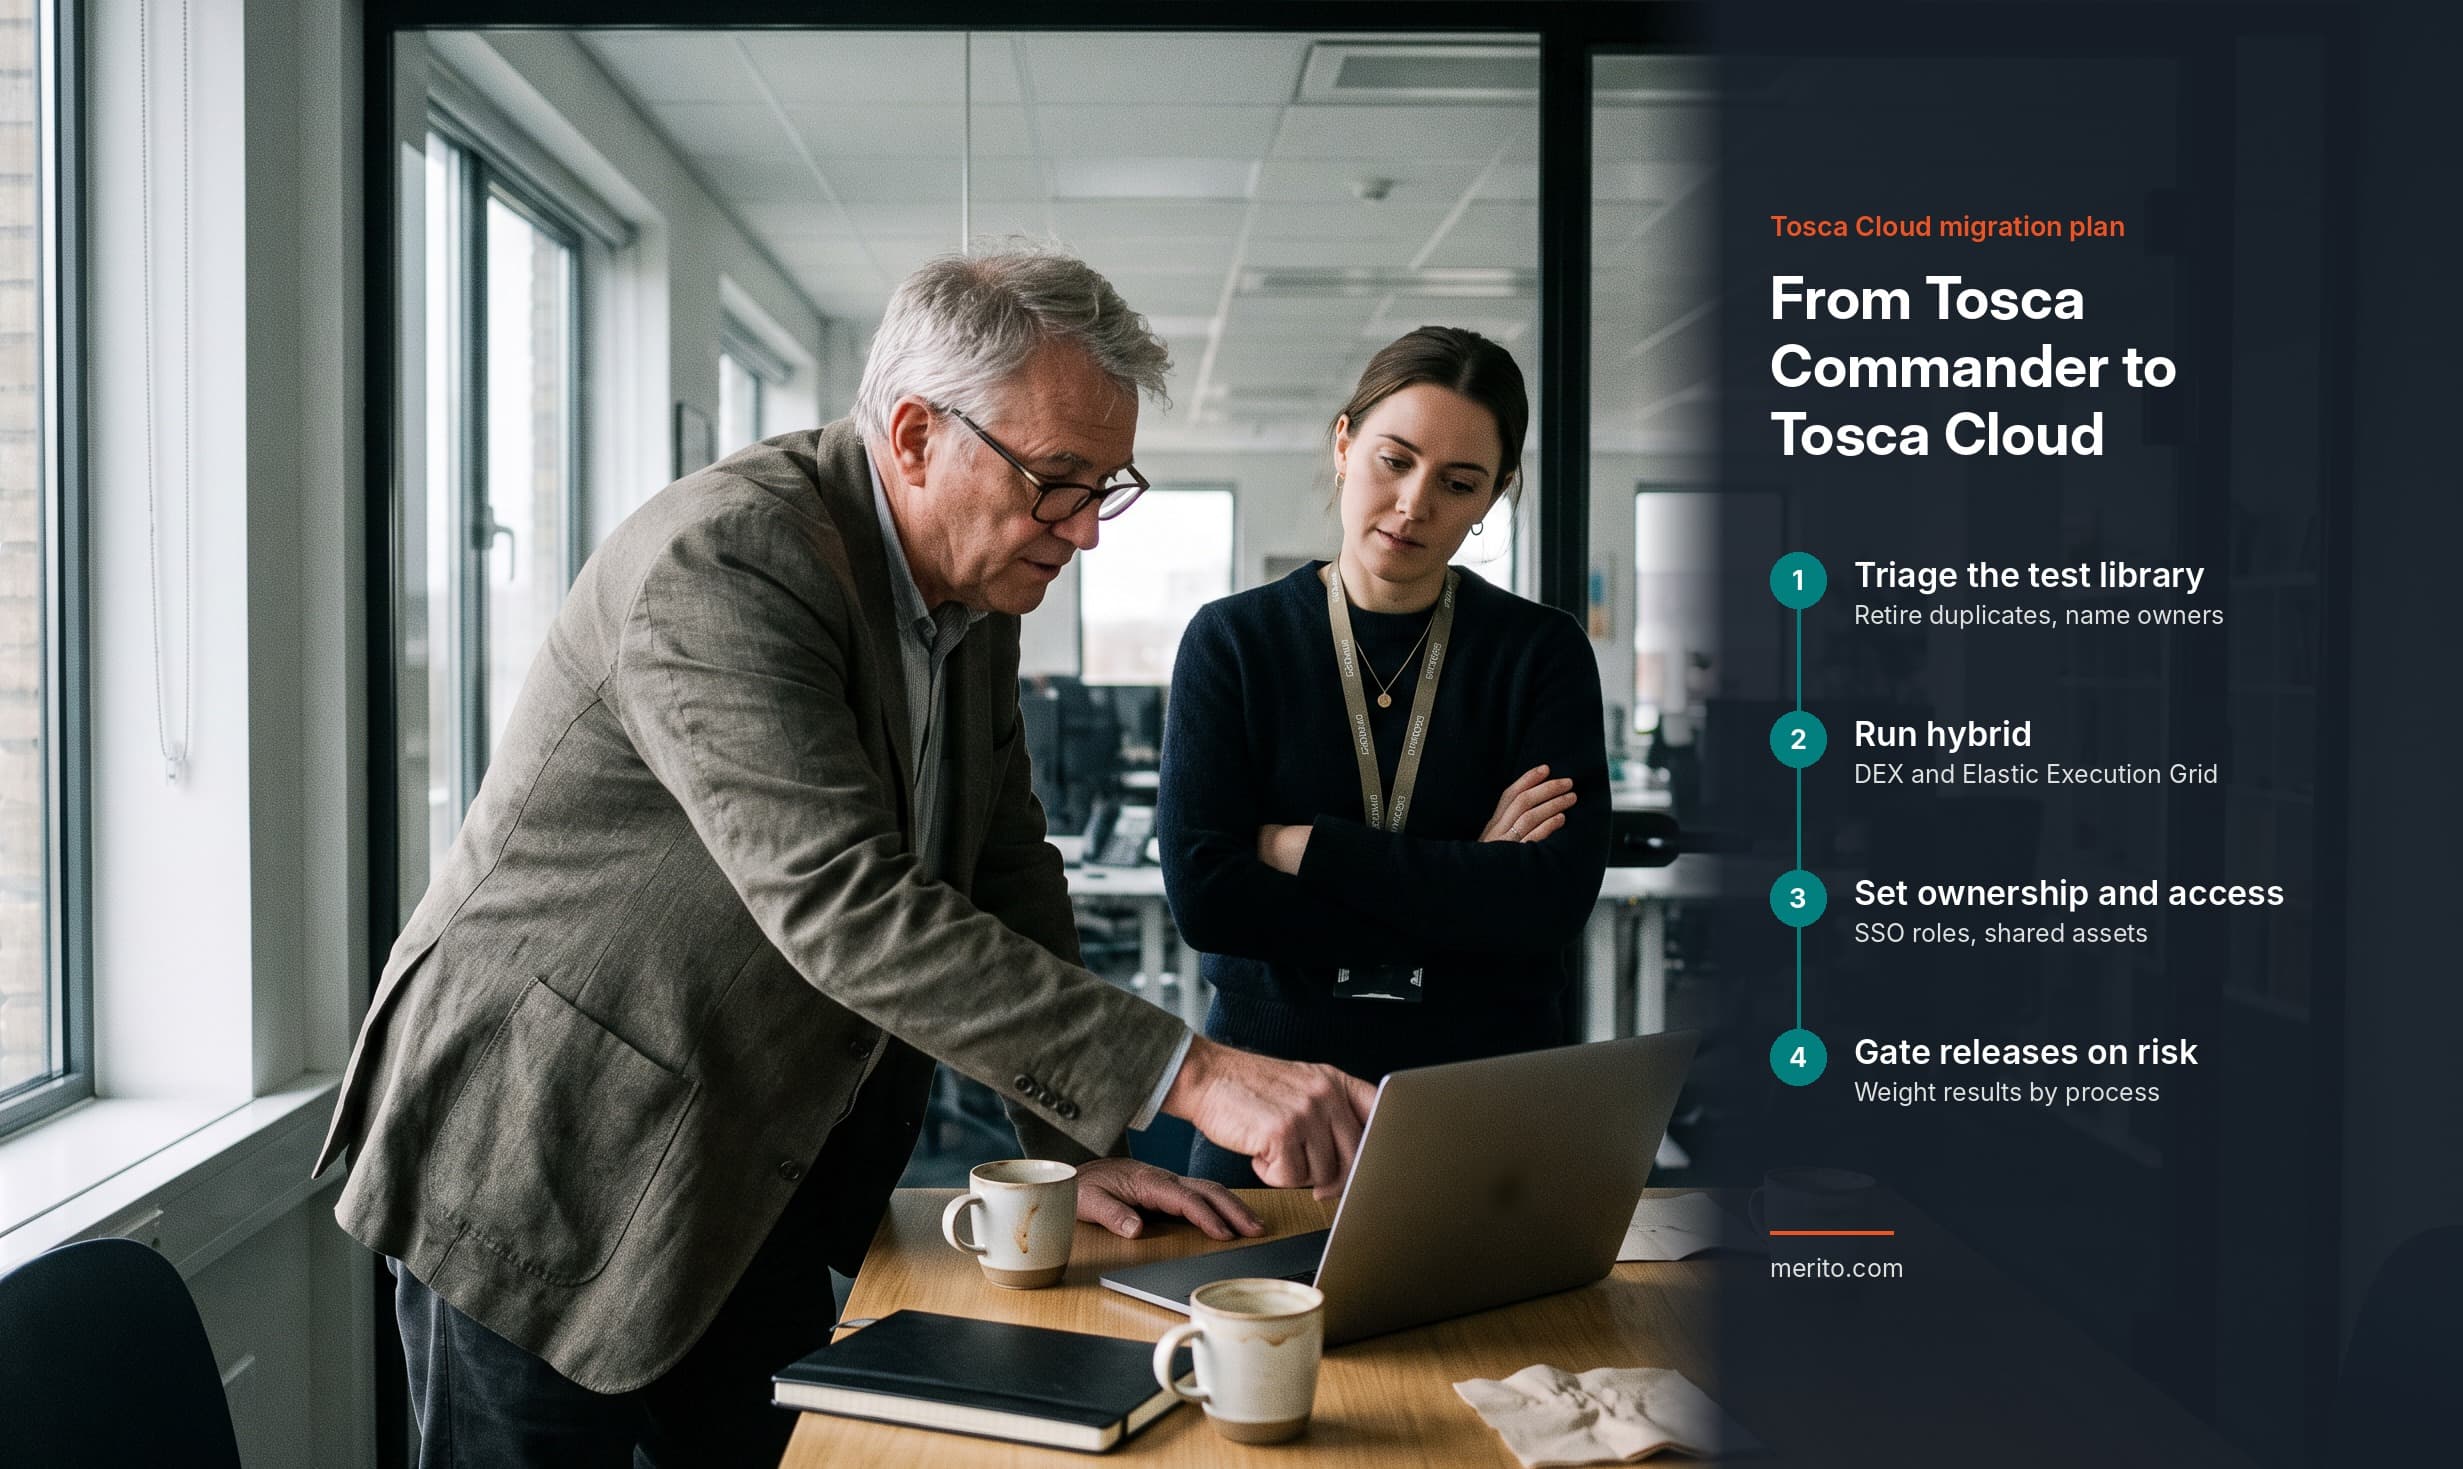
Two colleagues reviewing SAP release results on a laptop in a glass-walled meeting room, beside a four-step Tosca Cloud migration plan covering test library triage, hybrid execution, ownership and access, and risk-based release gates.
SAP Testing

Tosca Cloud Migration From Tosca Commander for SAP Testing Teams

A Tosca Cloud migration moves SAP test automation from Tosca Commander on company servers to the Tricentis-hosted SaaS version of Tosca. Teams can upgrade on-prem to Tosca 26.1 in about 10 to 14 weeks or migrate to Tosca Cloud in about 12 to 22 weeks. A phased plan triages the test library, runs DEX and Elastic Execution Grid in hybrid, assigns ownership, and connects results to release gates. Merito delivers this work as a Tricentis Certified Solution Partner.

  • Tricentis Tosca
  • Tosca
  • Tricentis
  • SAP Testing
  • SAP Test Automation
  • Test Automation
  • CI/CD
  • Migration Testing
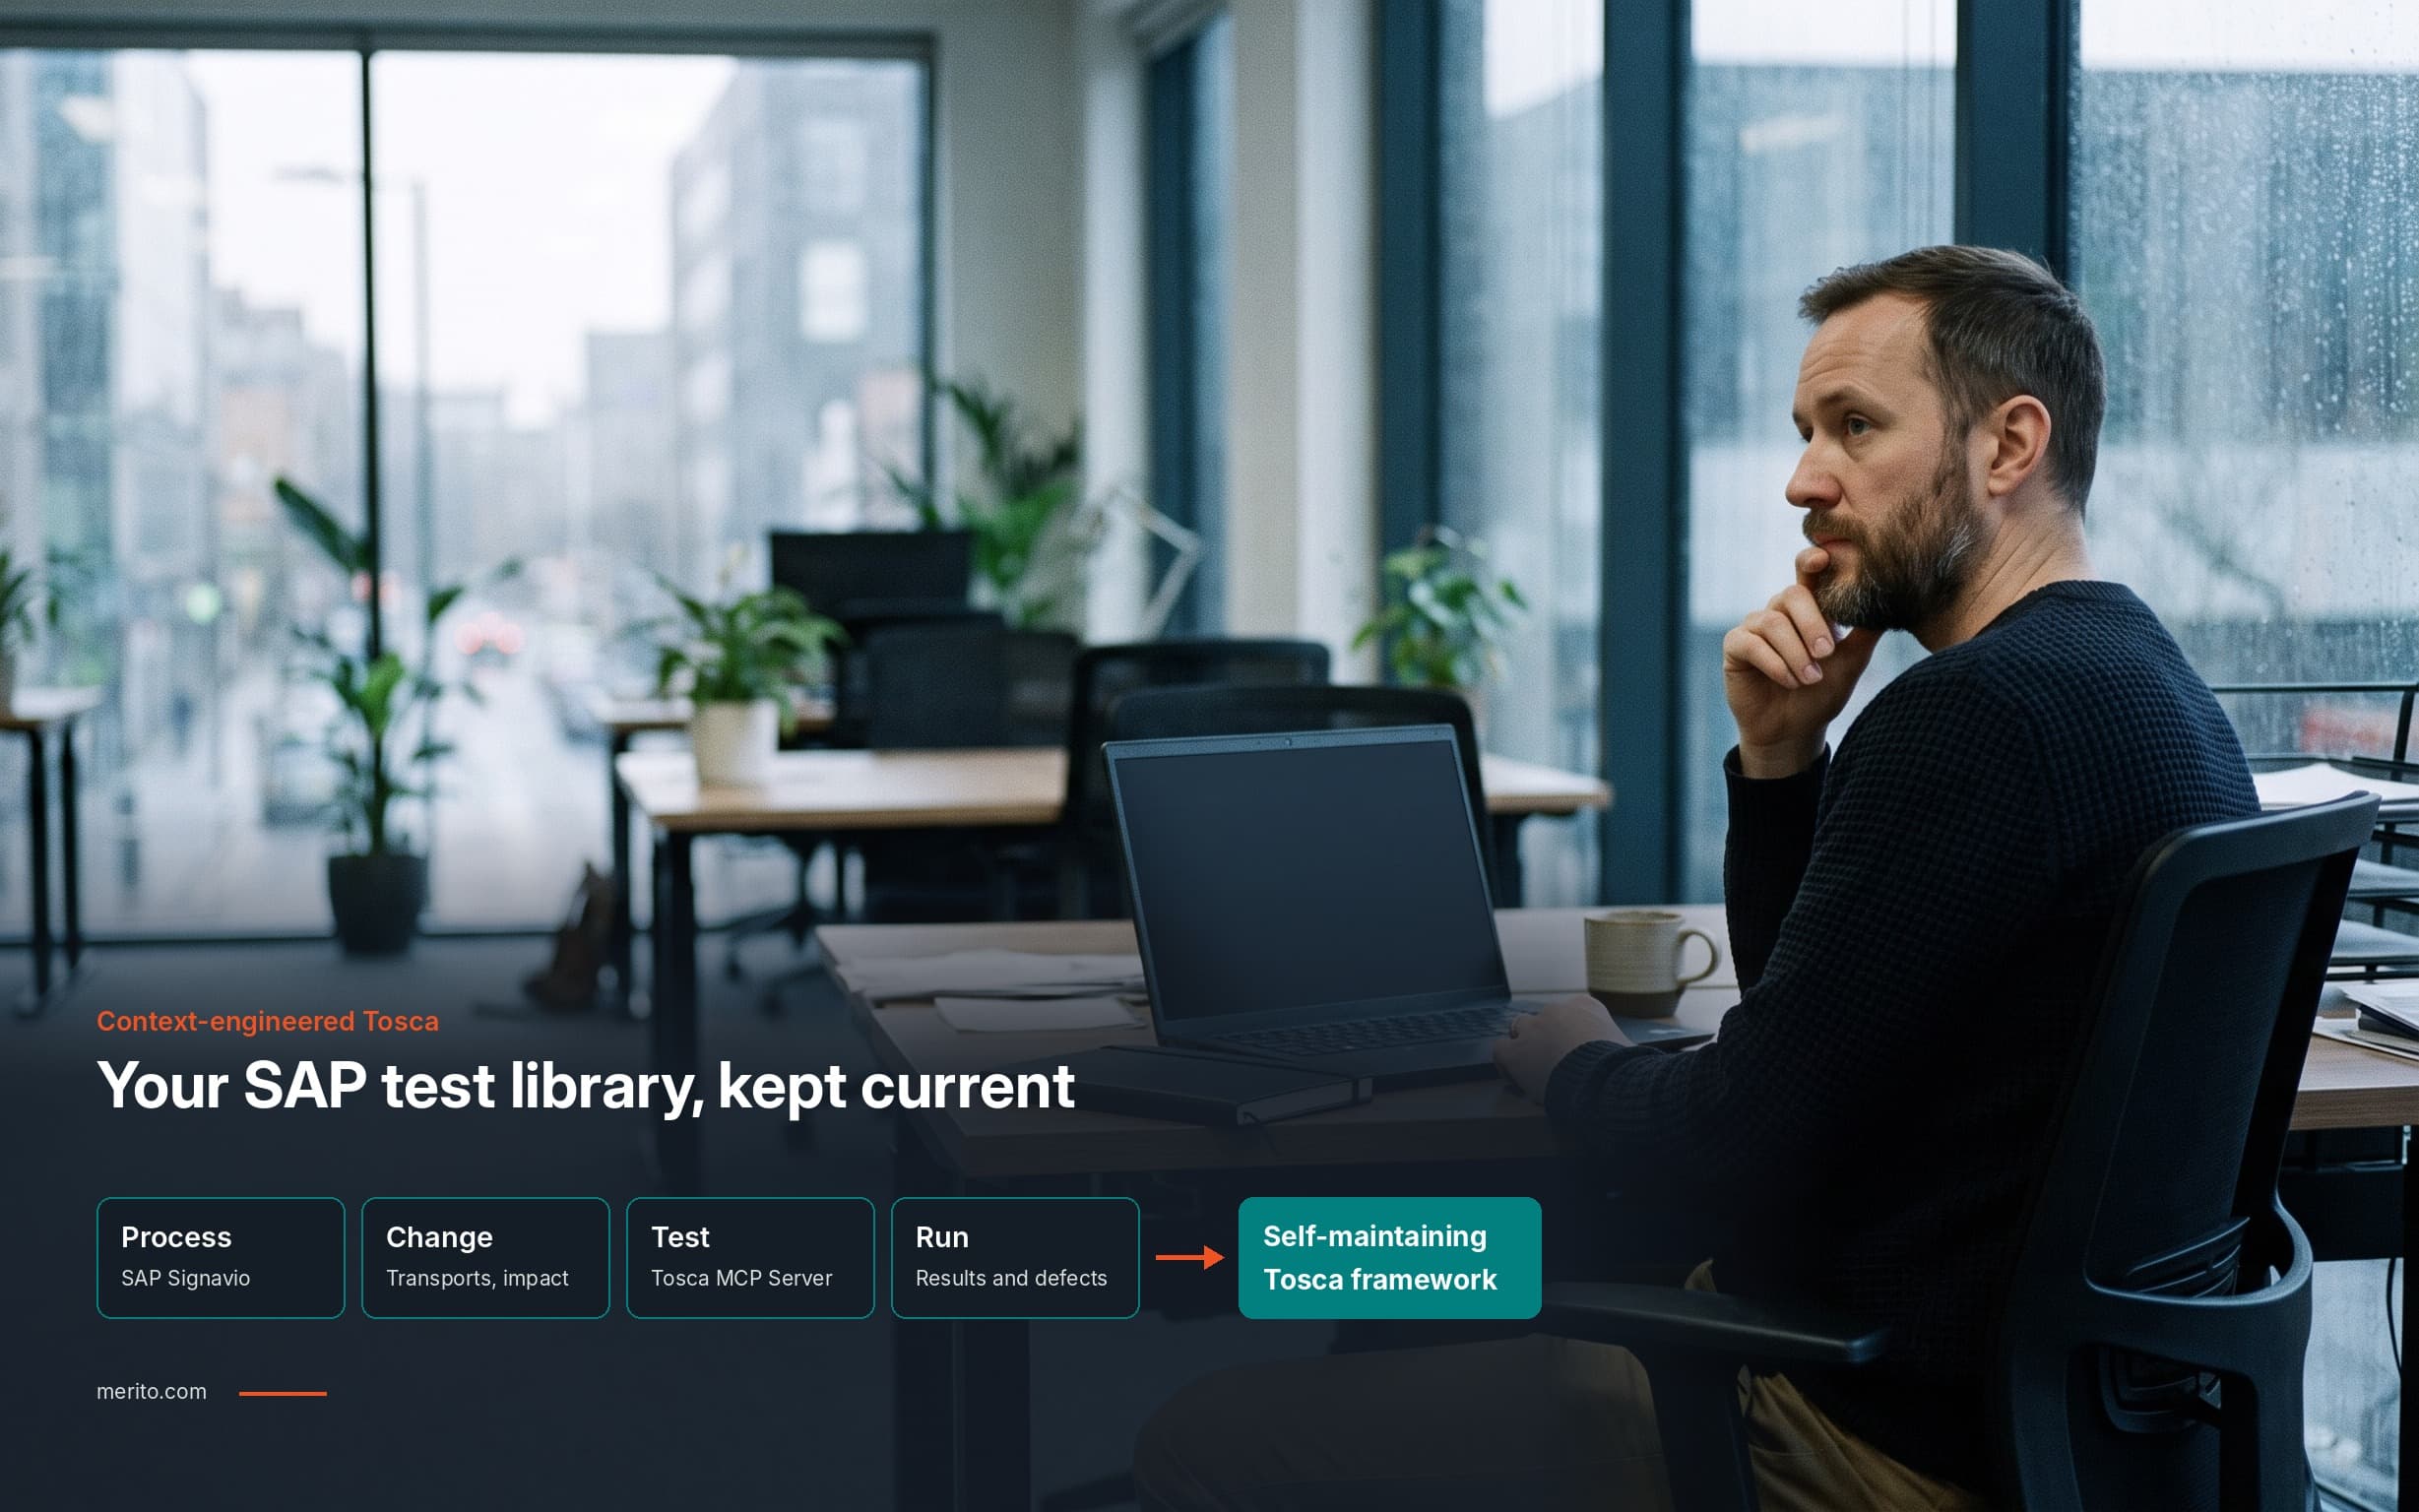
An SAP test engineer at a desk in a quiet office, thinking beside a laptop, with a diagram showing process, change, test, and run context feeding a self-maintaining Tosca test framework.
SAP Testing

Your SAP Test Library Starts Aging the Day You Build It

SAP test libraries go brittle as transports, support packages, S/4HANA programs, and Fiori updates change the system, and go stale as tests drift from the live business process. Merito pairs Tricentis Tosca and SAP Enterprise Continuous Testing with Claude and context engineering. Claude reads process context from SAP Signavio, change context from transports and Tricentis LiveCompare, test context through the Tosca MCP Server, and run context from results, so the framework hydrates test cases, retires stale tests, runs root cause analysis, and proposes Module repairs for human approval.

  • Tricentis Tosca
  • Tosca
  • Tricentis
  • SAP Test Automation
  • SAP Testing
  • Test Automation
  • S/4HANA
  • AI
  • Enterprise AI
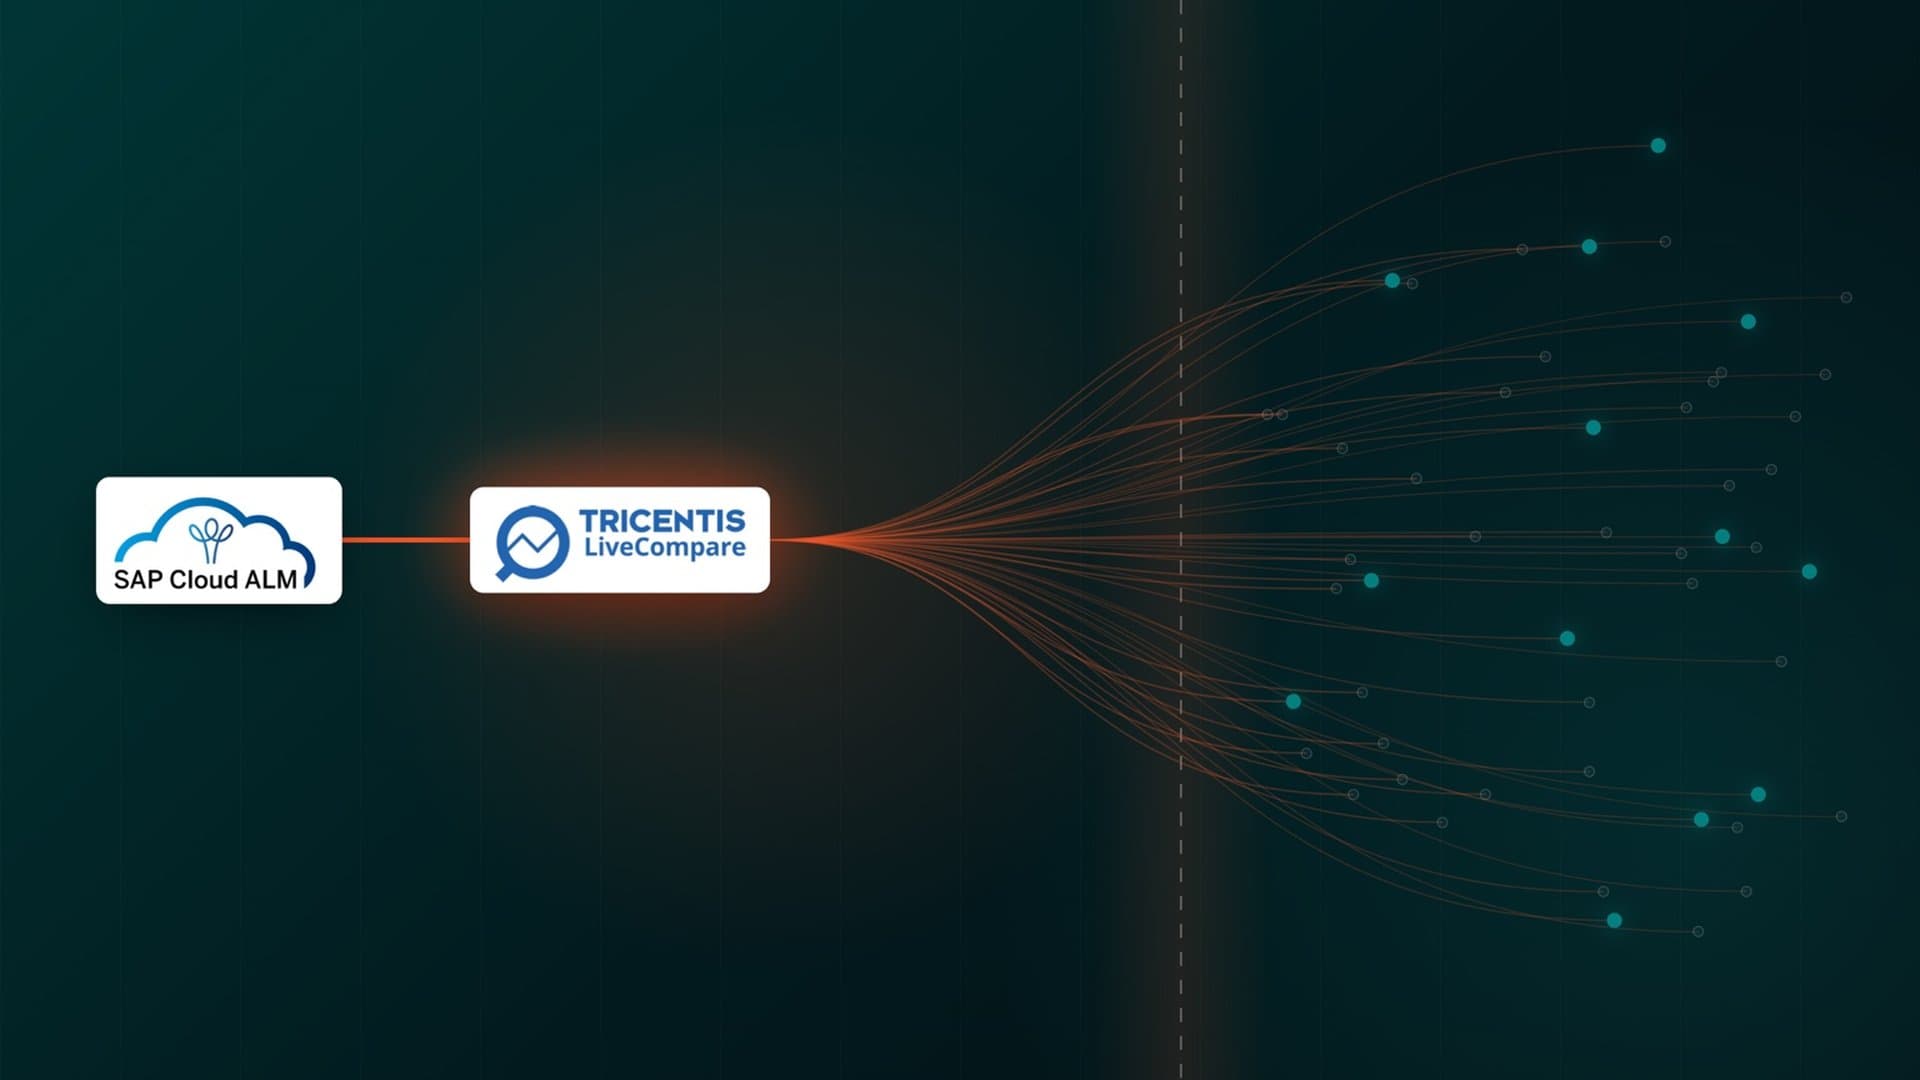
SAP Cloud ALM feeding Tricentis LiveCompare to analyze SAP transport changes and identify affected business processes for targeted testing.
SAP Testing

You Test Everything Because Nobody Can Prove What the Transport Touched

SAP Change Impact Analysis (CIA), sold by Tricentis as LiveCompare, reads a transport, support pack, or upgrade delta and resolves every dependent object down the call structure, standard SAP code included. It weights that dependency graph with production usage so objects nobody calls drop out of scope, then matches the result against test repositories such as Tosca, qTest, or Solution Manager to return covered objects and coverage gaps. Run on every transport cycle it makes a SAP Cloud ALM release gate enforceable instead of a signature field.

  • SAP
  • S/4HANA
  • SAP Upgrade
  • Tricentis
  • SAP Testing
  • Test coverage
  • Audit
  • Compliance
  • SDLC
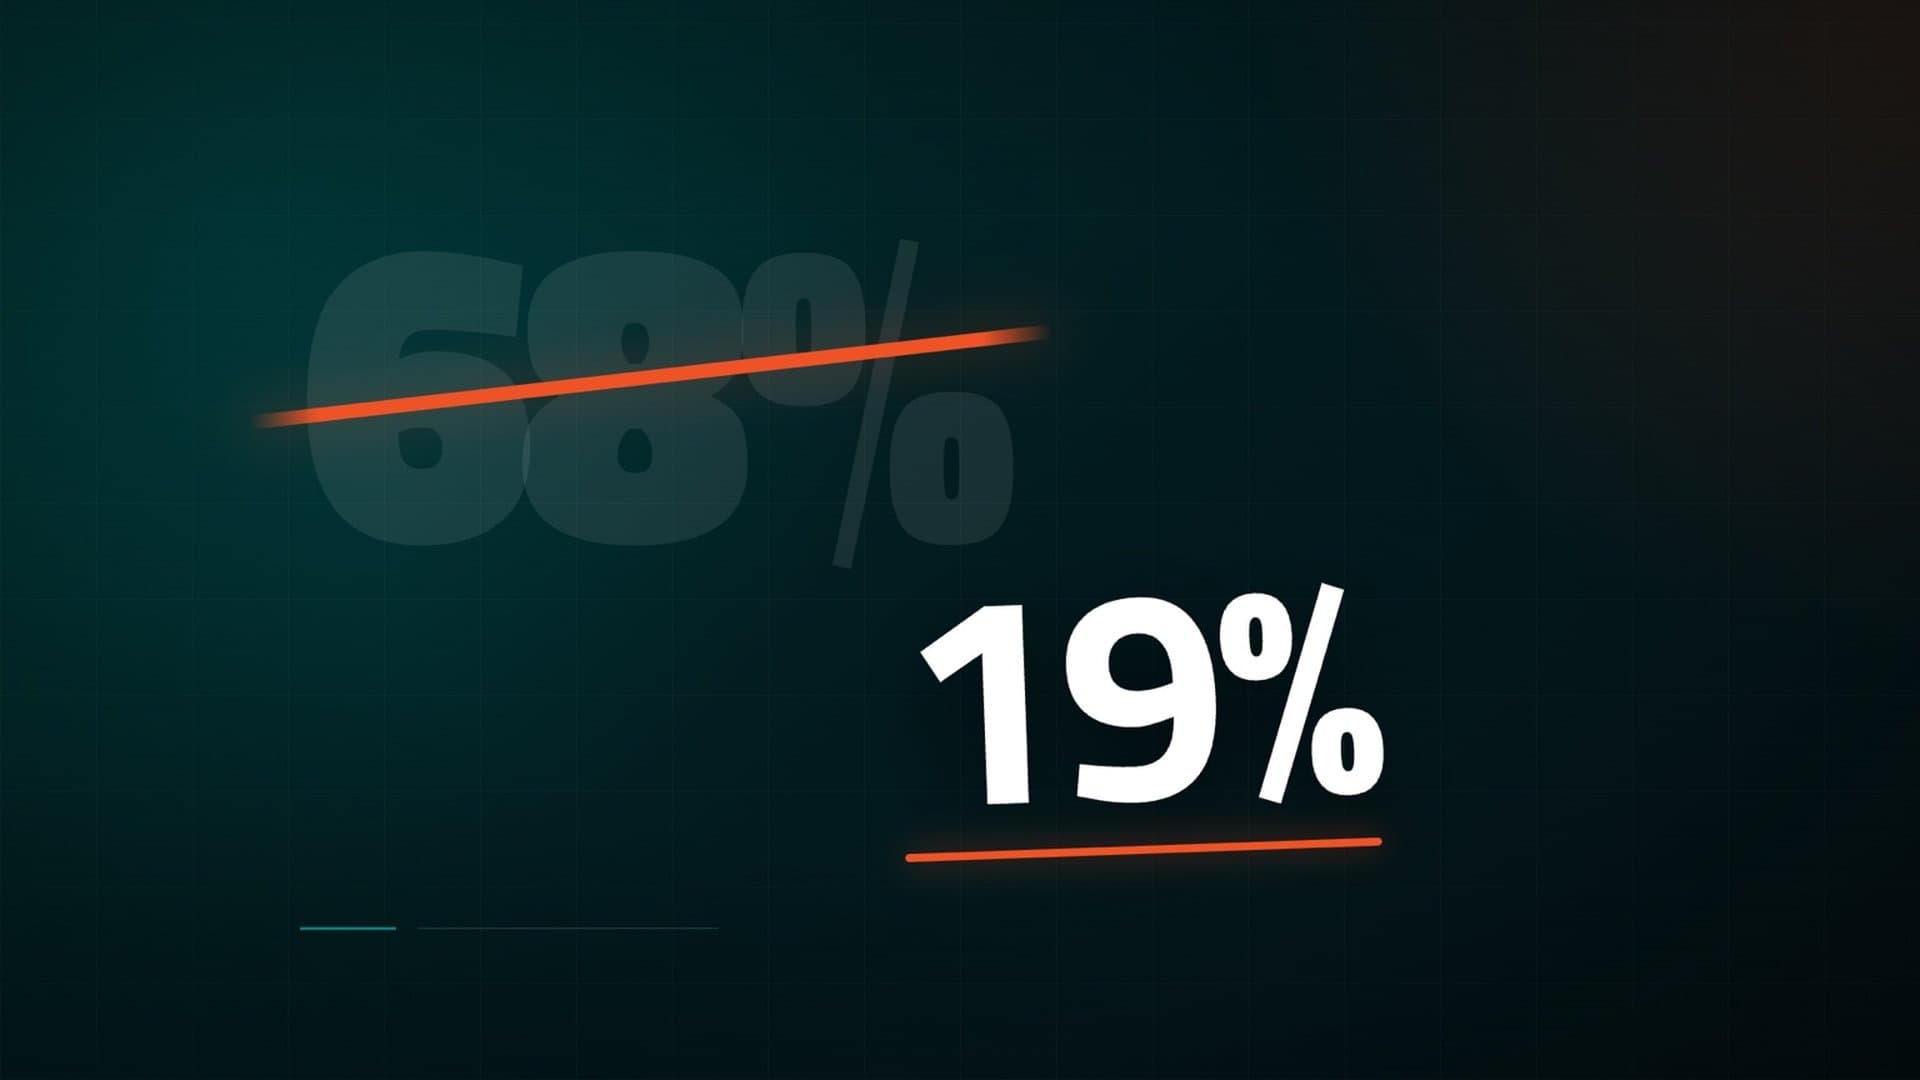
Graphic showing a 68% value crossed out and replaced with 19%, illustrating a significant reduction or improvement in an application quality metric.
SAP Testing

Your SAP Change Impact Business Case Needs Five Numbers, and None of Them Come From a Vendor

A business case for SAP change impact analysis should rest on five numbers the team produces itself: the fully loaded cost of one regression cycle, the number of cycles run per year, the share of test cases that exercise an object a transport actually changed, a scope reduction the team would defend to a CFO, and the price of one escaped defect. Vendor-published ROI percentages collapse under finance scrutiny because they trace back to a product page rather than the buyer's own program, and the escaped-defect line is usually the largest item in the model.

  • SAP
  • SAP Test Automation
  • SAP Upgrade
  • Tricentis
  • Procurement
  • Software Licensing
  • Enterprise Testing
  • Compliance
Jaguar SUV climbs rock face
SAP Testing

SAP Test Automation and Merito MAPS Could Have Saved Jaguar Land Rover from CVE-2025-31324

CVE-2025-31324 is a useful case study for automation engineers because it shows how exposed services, missing authentication, executable upload paths, and weak validation can turn a vulnerability into a business outage. The core lesson is not just AppSec scanning. It is that SAP test automation should include negative security scenarios that verify controls fail safely on every release. Merito MAPS helps teams identify those gaps, prioritize the right controls, and operationalize them in the delivery pipeline.

  • SAP Test Automation
  • SAP Security
  • Negative Testing

Frequently Asked Questions

Questions about the Merito blog