Insights

Merito Insights

Fresh thinking on secure software delivery, DevOps best practices, and the people-first approach that powers our clients’ success.

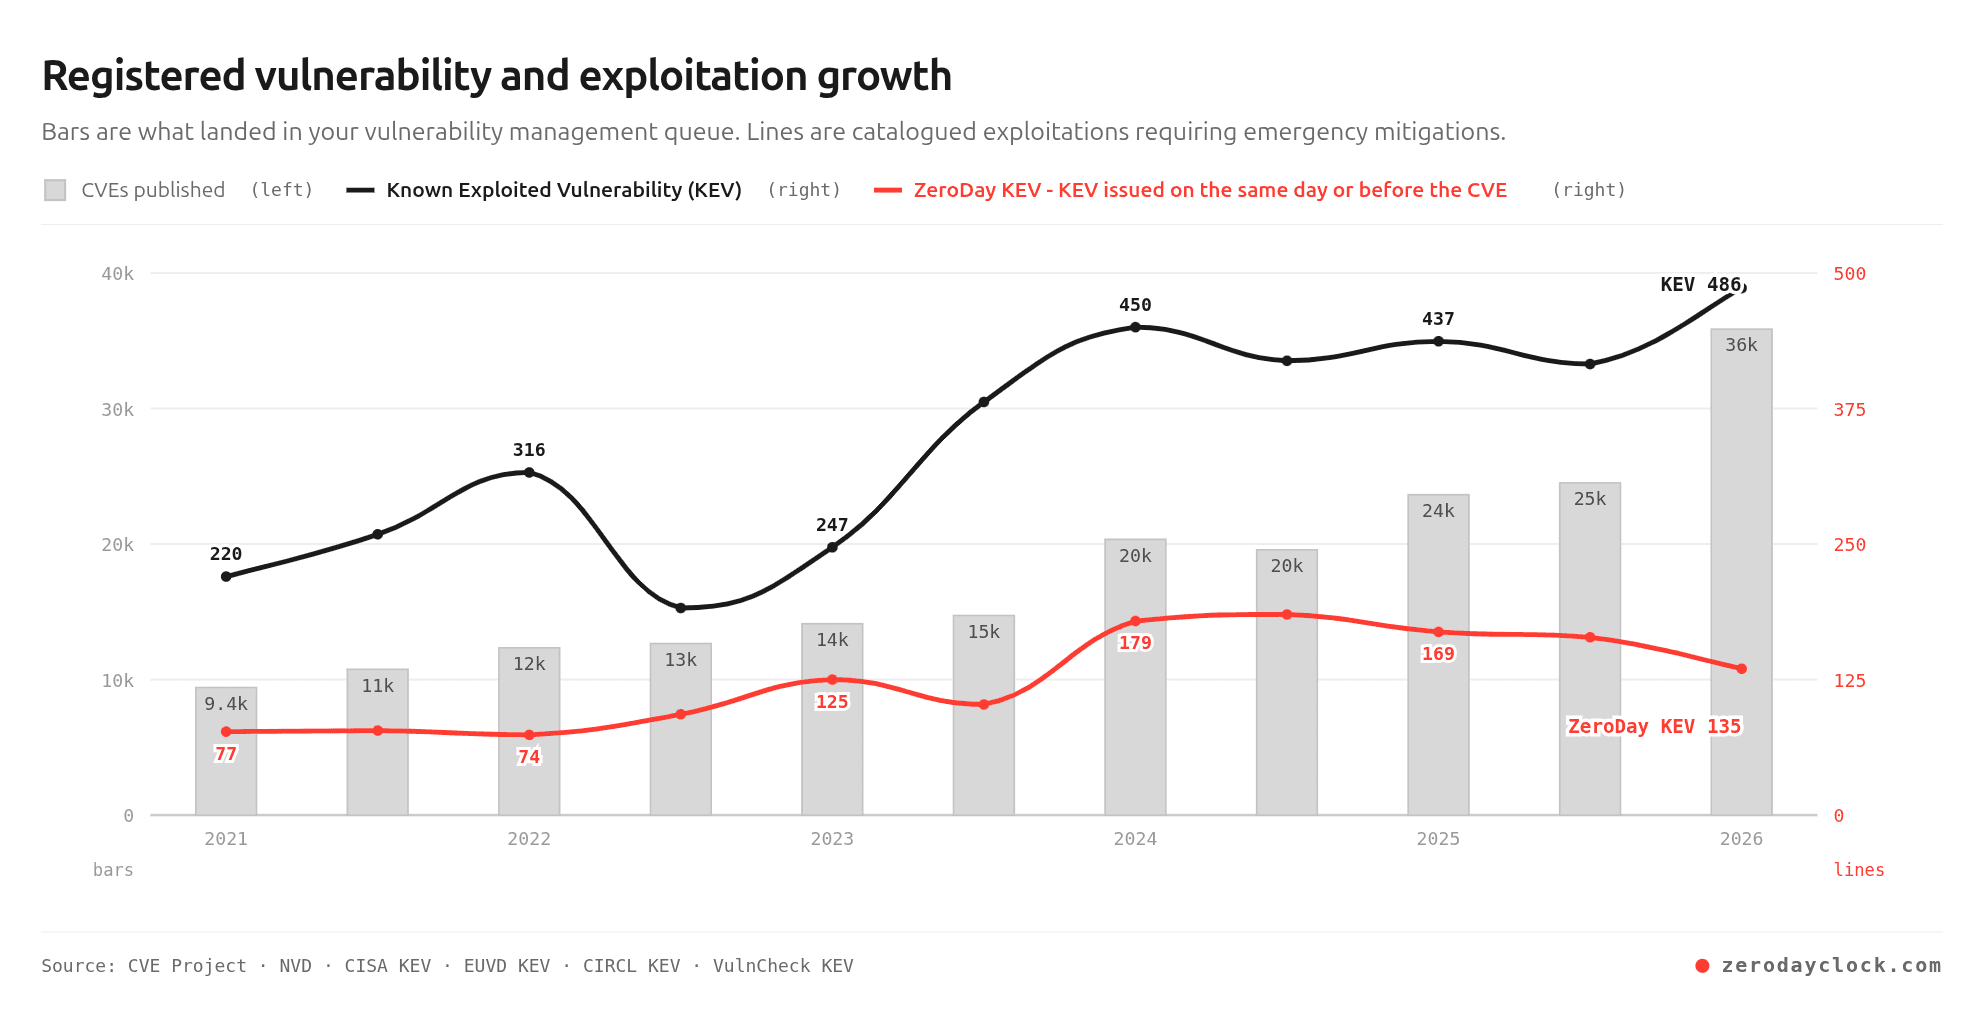
Chart from zerodayclock.com of registered vulnerability and exploitation growth from 2021 to 2026. CVEs published per half year rise from 9.4k to 36k while known exploited vulnerabilities (KEV) rise from 220 to 486.
Application Security and DevSecOps

Checkmarx Fusion: How Hybrid Scanning Raises SAST Accuracy

Checkmarx Fusion is a hybrid vulnerability detection layer in Checkmarx One that combines deterministic, rules-based SAST with a language-agnostic AI engine and curated frontier AI models, reconciled into a single result set. Checkmarx reports an F1 score of 0.741, versus roughly 0.20 for legacy rule-based SAST, and describes the approach as producing consistent results across scans while extending coverage to vulnerabilities with no existing rule or CVE.

  • Checkmarx
  • SAST
  • Application Security
  • DevSecOps
  • AI
Picture showing Engineer Protecting Against AI Cyber Threats with title "The 4 Things Every AppSec Vendor Now Ships, and the 4 We Still Need to Solve" and subtitle "Triage, autofix, IDE integration and grounded output are now table stakes. Re-testing, AI-BOM, mobile and agent guardrails will decide the next 12 months." with Blog Pill and Merito Logo
Application Security and DevSecOps

AppSec for the AI Era: What's Converged, and What's Still Taking Shape

AppSec vendors have converged on exploitability-scored triage, autofix pull requests, coding-agent integration, and grounded output, making those four things table stakes, not differentiators. Real competitive separation over the next 12 months will happen in four unsolved areas: continuous re-testing after a fix ships, AI-BOM, mobile AppSec keeping pace with embedded AI, and agent guardrails that enforce policy at the execution harness, not just the agent's decisions.

  • Application Security
  • AI
  • AI Coding
  • DevSecOps
  • SBOM
  • SCA
  • Compliance
vendor support to resolve a software application ticket
Application Security and DevSecOps

Deepsec Shows Why the Security Checkbox Was Never Enough

Security teams need more than code scanning. Explore how deepsec fits into a modern AppSec strategy with ASPM, DevSecOps governance, and layered validation.

  • deepsec
  • SCA
  • SAST
  • DAST
Computer with code on screen
Application Security and DevSecOps

Application Security in the Age of Agentic Coding: Why Software Bills of Materials (SBOMs) Matter More Than Ever

As agentic coding systems and AI-assisted development reshape software creation, understanding what goes into your codebase is no longer optional—it’s essential. Software Bills of Materials (SBOMs) have become the cornerstone of transparency and trust in modern application security, helping organizations mitigate risks introduced by complex, AI-generated dependencies.

  • AI
  • Application Security
  • SBOM

Frequently Asked Questions

Questions about the Merito blog